Your files, recoverable even when the office is down.
AmbraVault copies your file server every hour into an encrypted archive that cannot be changed, in your own AWS account, in Europe. To get the files back you need any computer, an internet connection and the authenticator app on your phone.
- 1 hour
- maximum age of the latest archive
- 30 days
- minimum period in which nobody can delete a copy
- 2 EU regions
- primary copy and replica, each with its own key
- 0 ports
- open for inbound traffic on your server
What AmbraVault is
A backup vault for file servers, installed in the customer's own AWS account. Four facts, none of which depends on you configuring it well.
A copy every hour
An agent on the Windows server copies the files every hour, open ones included (VSS). It sends only what changed and encrypts it on the server, before it leaves.
Copies that cannot be changed
Every copy stays locked for at least 30 days (S3 Object Lock in compliance mode). During that time nobody can delete it or shorten the lock, not even the account administrator.
In your account
The data stays in your AWS account, in European Union regions, with a replica in a second region. Soolutions installs and maintains the service but cannot read the content.
Every recovery leaves a trace
Whoever downloads gives a reason and confirms with a code. The log cannot be altered, and the people responsible get an email for every download.
Three steps, from any computer
Recovery does not go through the server, the office network, the VPN, Active Directory, Microsoft 365 or company email. It works when none of them is available.
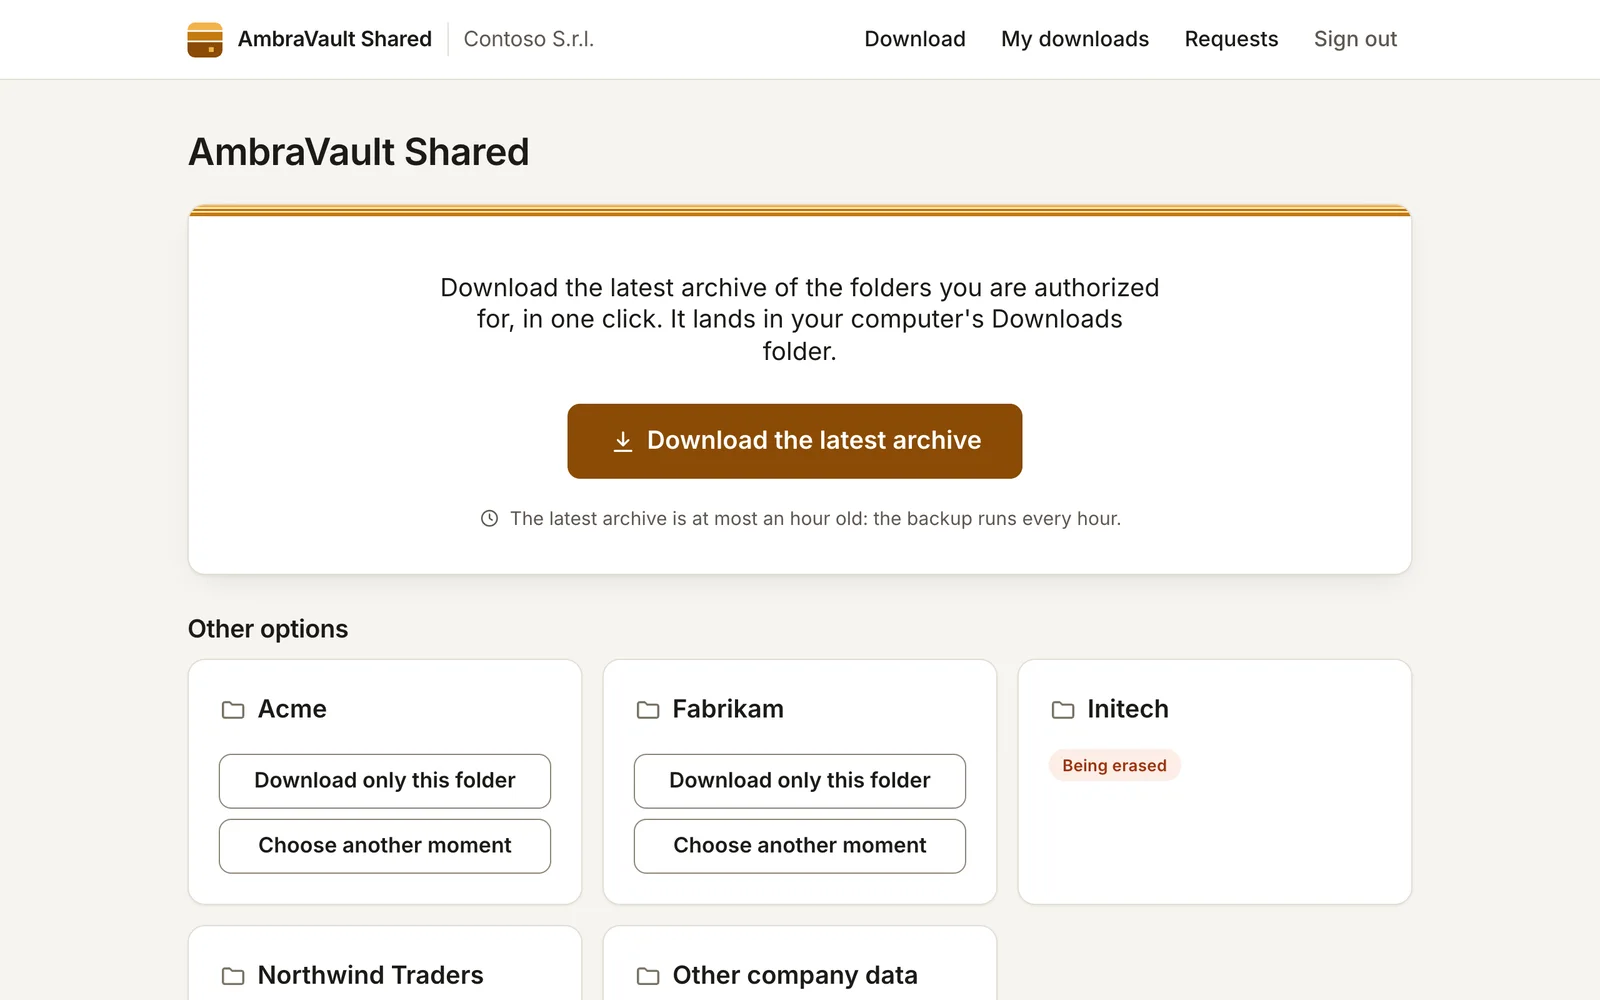
Sign in
From any computer, open your installation's address, for example
contoso.ambravault.com. Sign in with email, password and the 6-digit code from the authenticator app.“Download the latest archive”
One button, at the top of the page. Give the reason and confirm with a fresh code. Or pick another moment, a folder or a single file.
The file is in your browser
The zip lands in the Downloads folder, with its SHA-256 fingerprint. The people responsible get an email; the log keeps who, when, what and why.
“A disaster recovery that needs the original infrastructure is not a disaster recovery.”
Built for those who hold other people's data
Many products do backup well. AmbraVault was designed starting from recovery, accountability and erasure.
Recovery without the office
Recovery needs none of the customer's systems. Sign-in is separate from your company identities: an attack on Active Directory or on email does not open the way to the backups.
The operator cannot read
Soolutions installs and updates the service, but its role cannot decrypt the data or read the keys, and cannot create users in your place. The residual risk is stated openly in the technical documentation.
Erasure per client
The data of each of your clients can live in a partition with its own key. Once the key is destroyed, that data can no longer be read by anyone. Two people must approve; at the end you receive a PDF statement (NIST SP 800-88 method).
An agent that takes no orders
No port opens on the server and no remote command runs. The agent's identity is a non-exportable key in the TPM chip, with a certificate issued by your own authority. Configuration and updates are signed.
Independent layers
Whoever gets past one layer meets the next. The security level is the same in every plan: always the highest.
If ransomware hits the server
The agent can add data to the archive; it cannot delete or modify it. Copies already written stay locked for at least 30 days. A backup full of files changed in bulk raises an immediate alert, and if backups stop, an email follows within a few hours.
AmbraVault is not “certified” and not “ransomware-proof”. The security certifications belong to the AWS services it is built on. restic's cryptography has been publicly reviewed, not formally audited.
| On the server | Encryption before upload (restic: AES-256 and Poly1305), with a random 256-bit password per partition, never chosen by a person. |
|---|---|
| In AWS | A second encryption layer with customer-managed KMS keys; keys in FIPS 140-3 validated hardware modules; key deletion denied by policy. |
| In transit | TLS 1.2 or later only, HSTS. |
| Immutability | S3 Object Lock in compliance mode, at least 30 days, on the primary copy and on the replica. |
| Access | Authenticator code required for everyone, again before every download; 15-minute sessions; a WAF in front of the app. |
| Emergency | A sealed spare copy of every password, with hybrid post-quantum encryption; the key that opens it is split into three shares, any two of which suffice. |
| Oversight | Hash-chained log, copied to immutable storage; an email for every download; a second person's approval for every erasure and, if enabled, for downloads above a threshold. |
Organisations that answer for the data they hold
Firms and companies of 10 to 250 people, and the IT partners who look after them.
Professional firms
Accountants, lawyers, consultants, engineering and architecture studios. Client data to keep, to hand back and, when the engagement ends, to erase in a documented way.
Practices and companies
Organisations with a file server on site and no IT department. They need a backup that works without daily attention and a recovery that any authorized person can carry out.
IT partners
About 30 minutes per server to install, signed scripts, no port to open. If backups stop, the partner and Soolutions get an email.
AmbraVault helps document the security measures and data access that the GDPR and, where it applies, the NIS2 directive ask you to demonstrate: access log, periodic reports, the list of authorized people, erasure statements. It does not replace the data controller's own assessment.
How to start
Today AmbraVault protects file servers running Windows Server 2019, 2022 and 2025 with a TPM 2.0 chip. Linux and NAS are planned.
Account and address
Soolutions prepares the installation in your AWS account, in EU regions, and the address
<company>.ambravault.com.Agent on the server
The IT partner installs the agent with a signed script. The server's key is created in the TPM; your own authority signs its certificate.
First backup
The first copy is complete and can take a while. From then on the service runs every hour, on its own.
Handover
Authorized people set up the authenticator app. The three shares of the emergency key go to three different people.
Quoted on request
The Soolutions service is quoted on request, based on the data to protect. The security level is the same for every customer.
The AWS infrastructure is in your account and you pay AWS directly, with no always-on servers. The weekly report shows the real cost.
AmbraVault and the most common alternatives
A summary of capabilities that can be checked in public documentation. The alternatives do many things AmbraVault does not; the full page says so, with sources.
| Capability | AmbraVault | Veeam Backup & Replication with object storage | Acronis Cyber Protect Cloud | Synology NAS with Hyper Backup | Cloud sync (OneDrive / SharePoint, Dropbox) | LTO tape, USB disks |
|---|---|---|---|---|---|---|
| Copies that cannot be changed | Yes | If configured | If enabled | Depends | Not included by default | Depends |
| Data in a cloud account owned by the customer | Yes | Yes | Depends | If configured | No | Not applicable |
| The service operator cannot read the content | Yes | If enabled | If enabled | If enabled | Not included by default | Depends |
| Recovery without the original infrastructure | Yes | With a Veeam server | Yes, for files | Yes | Yes | With the hardware |
| Cryptographic erasure of one client's data, with a statement | Yes | Not documented | Not documented | Not documented | Not documented | No |
| Log and notification on every recovery | Yes | Depends | Log | Not documented | Log | No |
| Second-person approval | Yes | For deletions | Not documented | Not documented | Not documented | No |
| Agent identity bound to the TPM | Yes | Not documented | Not documented | Not applicable | Not applicable | Not applicable |
| Data in EU regions | Yes | Depends | Selectable | Depends | Depends | Depends |
Frequently asked questions
If Soolutions no longer existed, could we recover the data?
Yes. The data is in your AWS account, in an open format (restic). With two of the three shares of the emergency key and the standard restic program, the data can be recovered without AmbraVault and without Soolutions. The procedure is documented.
Can Soolutions see our files?
Not by design: files are encrypted on your server, and the role Soolutions uses to manage the installation is not allowed to decrypt. Whoever ships the software could in theory ship malicious code: that is why every release is signed, every change in the account is notified to you, and you can refuse or postpone an update.
What if I lose my phone?
An administrator of your organisation resets the authenticator from the app, after checking the person's identity by phone or in person. For an administrator, a second administrator is needed. Soolutions cannot reset access.
How old is the latest archive?
One hour at most, with the default schedule. You can also pick an earlier copy: by default 24 hourly, 14 daily, 8 weekly, 12 monthly and 2 yearly copies are kept.
Does AmbraVault also protect Microsoft 365 or virtual machines?
No. AmbraVault protects the files on file servers. Mailboxes, SharePoint sites or whole virtual machines need dedicated tools, which AmbraVault does not replace.
Where is the data?
Only in AWS regions of the European Union: the primary copy, for example, in Milan and the replica in Frankfurt. The configuration rejects regions outside the EU.
Let's talk
A 30-minute walkthrough, with the app running on sample data. For IT partners, also a trial installation.
Write to amministrazione@soolutions.io
We reply within one working day.